
The essential answer
Redundancy provides additional components or copies that can support continued availability. Backup preserves recoverable states for restoration. Their purposes overlap, but they are not interchangeable. Multiple live copies may all receive an unwanted change, while a retained earlier state may help recover from it. NIST's storage guidance treats protection and restoration as distinct concerns. The conceptual question is not merely how many copies exist, but which failures those copies are capable of surviving.
How to reason about it
A useful comparison begins with a failure scenario. If one device becomes unavailable, another current copy may help. If a mistaken edit propagates to every current copy, the number of synchronized copies may not solve the problem. A recovery history addresses a different question: can a suitable earlier state be restored? Both approaches depend on assumptions about separation, access, and restoration. Counting copies without examining shared dependencies can therefore produce false confidence. For teaching purposes, imagine each dependency as a link connecting otherwise separate boxes. A common account, location, or automated process can create a shared exposure. This is a logical risk model rather than a product recommendation. It shows why resilience must be evaluated against named events and demonstrated recovery capabilities.
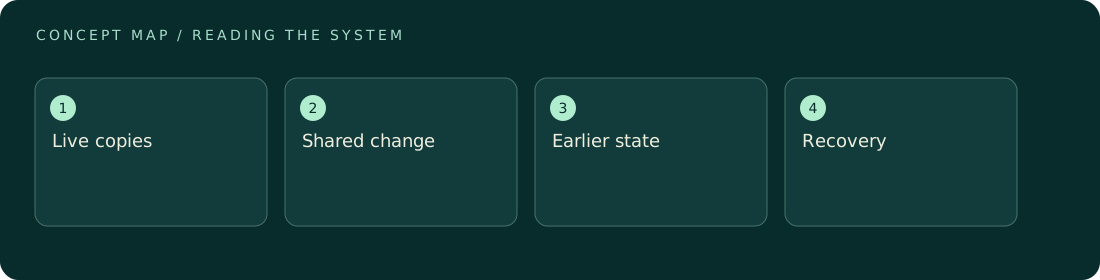
ILLUSTRATIVE · NOT A REPORTED RESULT
An example to work through
Assume a fictional project has three synchronized copies of a notebook. An accidental deletion is immediately synchronized to all three. There were three copies before the event and no current copy afterward. Now assume a separate history retains yesterday's notebook and can be recovered. That history addresses the deletion scenario, though it may omit today's legitimate changes. The example does not specify a backup schedule or endorse a service. It illustrates the tradeoff between recovering an earlier state and preserving the most recent work, and why availability and recoverability deserve separate questions.
Where interpretation fails
Avoid saying three copies means safe without identifying common dependencies and the relevant failure. A synchronized replica is not automatically a usable historical backup. Likewise, a stored backup is not demonstrated recovery until the ability to retrieve and interpret the needed state has been established.
The next decision
Describe the failure you want to understand, then ask whether the design supports continued access, historical recovery, or both. Look for evidence about restoration and shared dependencies. Compare claims against those scenarios rather than ranking archives by copy count alone or assuming one mechanism covers every loss.
Sources & context
These sources support the concepts noted below. Our synthetic examples and research framing are educational interpretation; they are not findings from these organizations or validation of our ventures.
- Security Guidelines for Storage Infrastructure ↗
NIST guidance distinguishes data protection, isolation, and restoration assurance.
Source check: Official PDF opened; overview reviewed, not a complete controls audit.
Educational research context, not a validated device specification or clinical protocol. Read our editorial and correction policy.